
https://tryhackme.com/room/splunkforloganalysis-aoc2025-x8fj2k4rqp
Created by: tryhackme, Dex01, 1337rce
In this room we get to help the SOC team for the The Best Festival Company (TBFC) with one of the most popular SOC tools: Splunk! You will spin up your virtual environment then launch the provided hyperlink to the Splunk SIEM in your browser. It might take couple of minutes to make a full connection. Though this room has a medium difficulty, it’s very guided and they break everything down if this is the first time you are using Splunk or need a refresher(like me!).
In order to filter out routine web traffic, such as Mozilla and Chrome, THM has us use this filter.
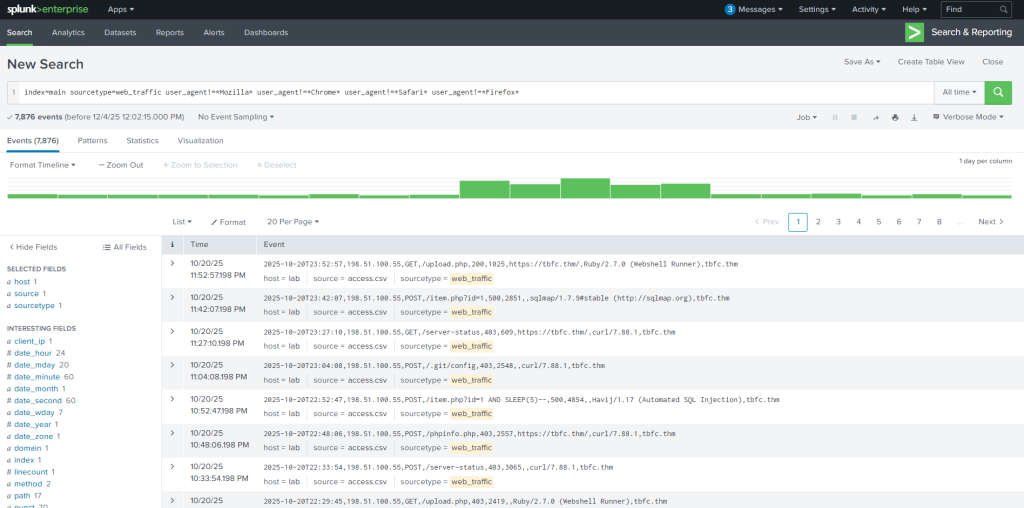
With the next step instructed, we have obtained our first answer for the question, “What is the attacker IP found attacking and compromising the web server?”

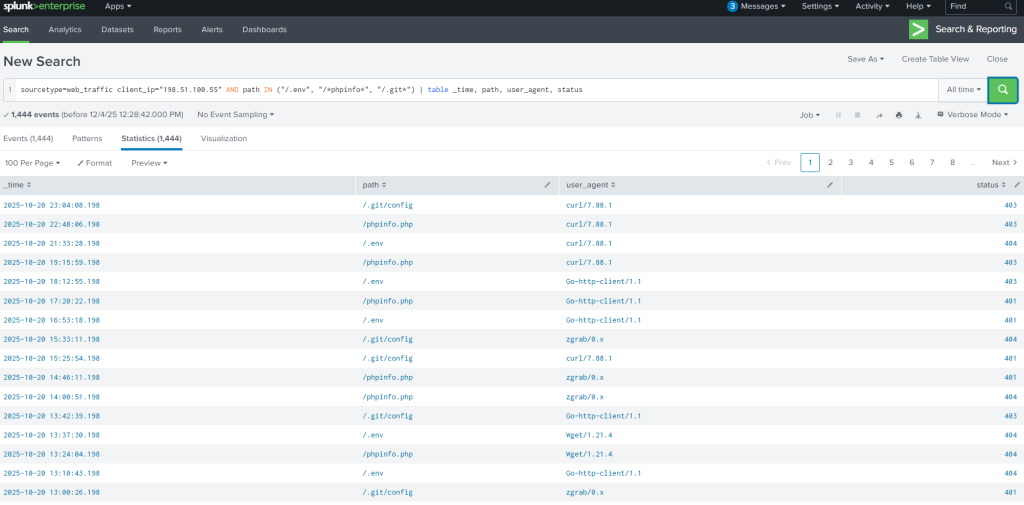
Now that we know the IP source of the evil bunnies, it’s time to narrow down our search! THM gives us various search queries to use to look at different things.
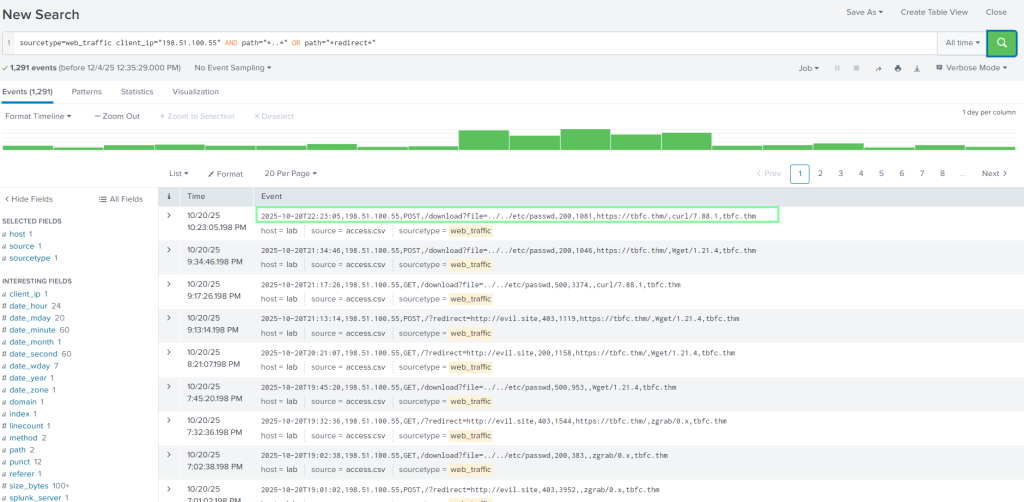
Path traversal!
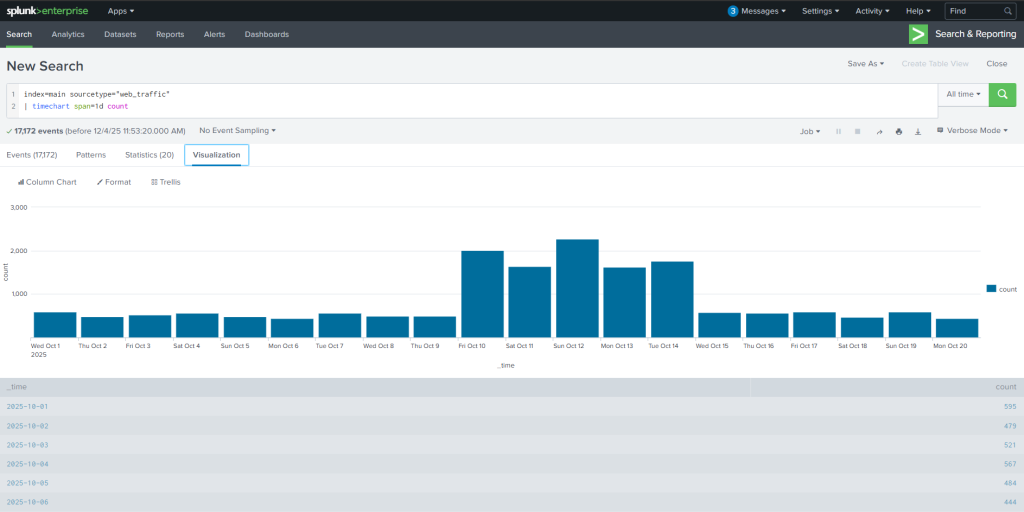
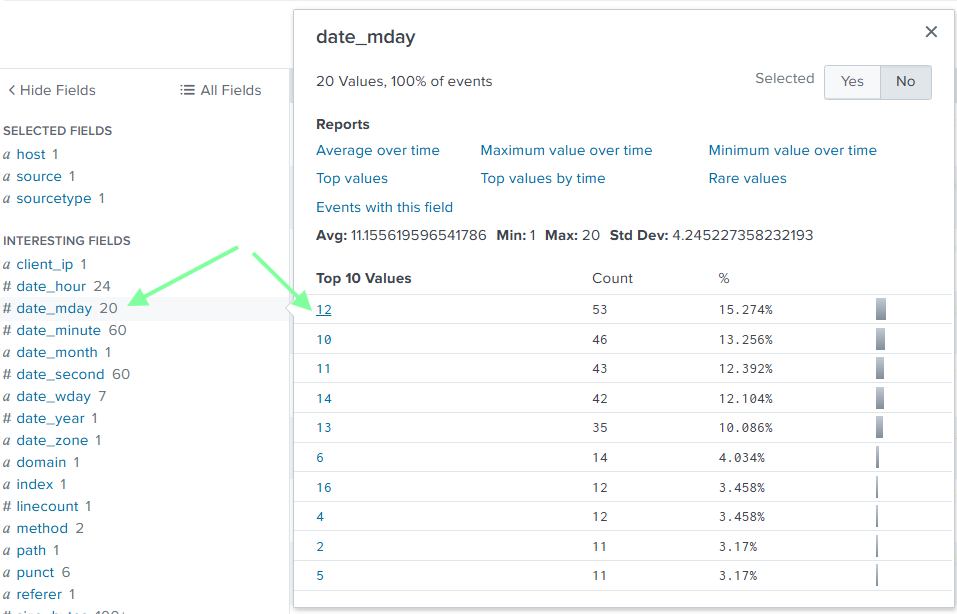
There are various ways of coming across the answer for the 2nd question, “Which day was the peak traffic in the logs? (Format: YYYY-MM-DD)”, But when you are on any of the longer filters that THM provides, go back under Events and click date_mday > 12.

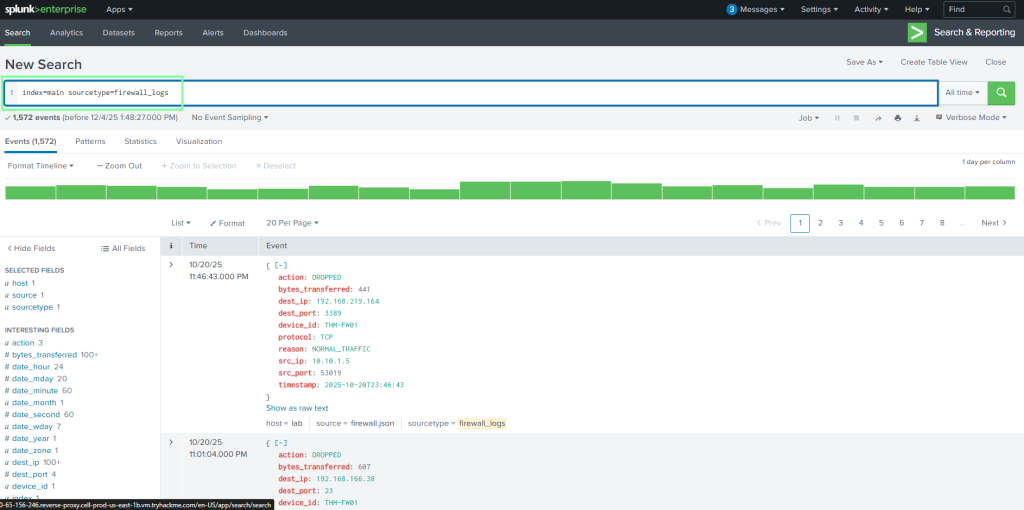
Looking at the firewall logs.
Going out of order, but with the last filter given, this is the answer to the question of “Examine the firewall logs. How many bytes were transferred to the C2 server IP from the compromised web server?”

For the question, “What is the count of Havij user_agent events found in the logs?” I combined various filters. You could also do “stats count by user_agent.”
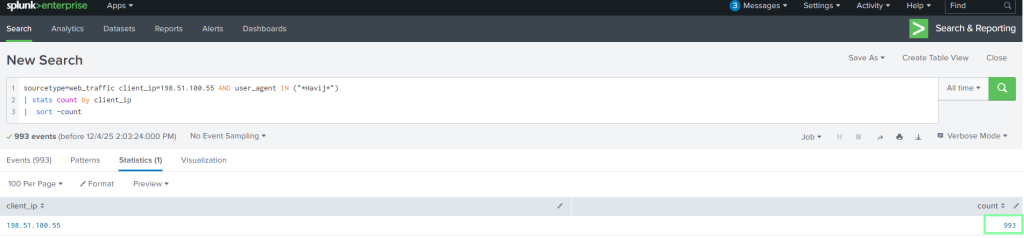
For “How many path traversal attempts to access sensitive files on the server were observed?”, I used a previous command from earlier.
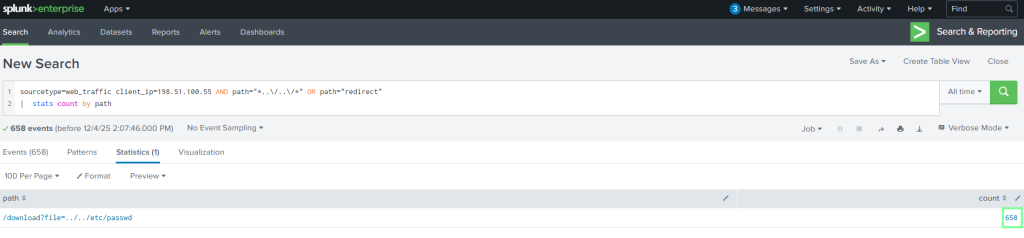
And that’s it! Of course, with the Advent of Cyber rooms, THM has various cyber enthusiasts cover the rooms, and I definitely recommend MadHats video coverage of the room. He breaks down everything more than the room itself does, and it’s only 16 minutes: https://www.youtube.com/watch?v=0cuAsDTfNbA. THM also links to another Splunk room(apparently over 300 minutes to finish it, so that’s a lot of Splunk content!) https://tryhackme.com/room/splunk201.