https://tryhackme.com/soc-sim/scenario-onboarding
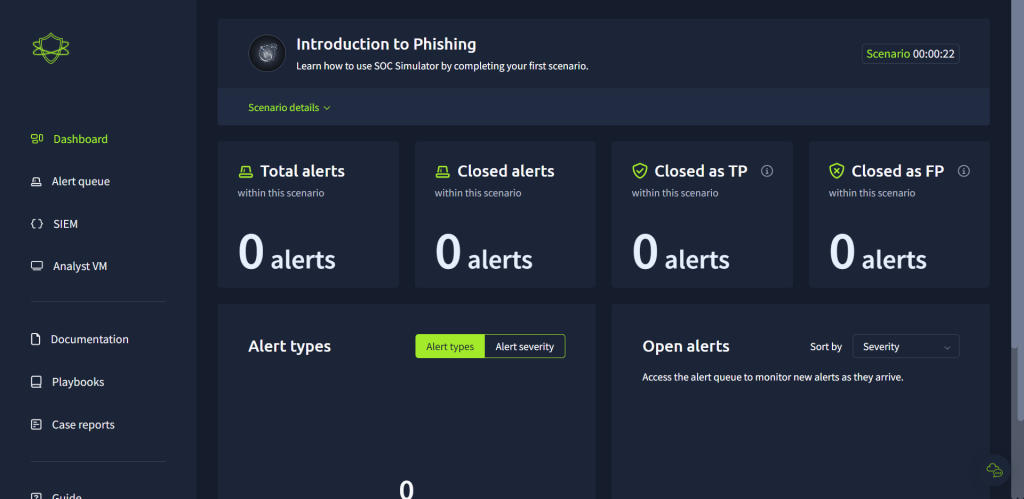
“Learn how to use SOC Simulator by completing your first scenario. Close all True Positive alerts to pass!”
This is the first time being in the SOC Simulator. I’m excited as I have heard good things and have seen emails involving the updates with this the past couple of years. When launching this, you get a chance to select your SIEM. I went with Splunk. Remember your 5 W’s when tackling this: Who, What, When, Where and Why.
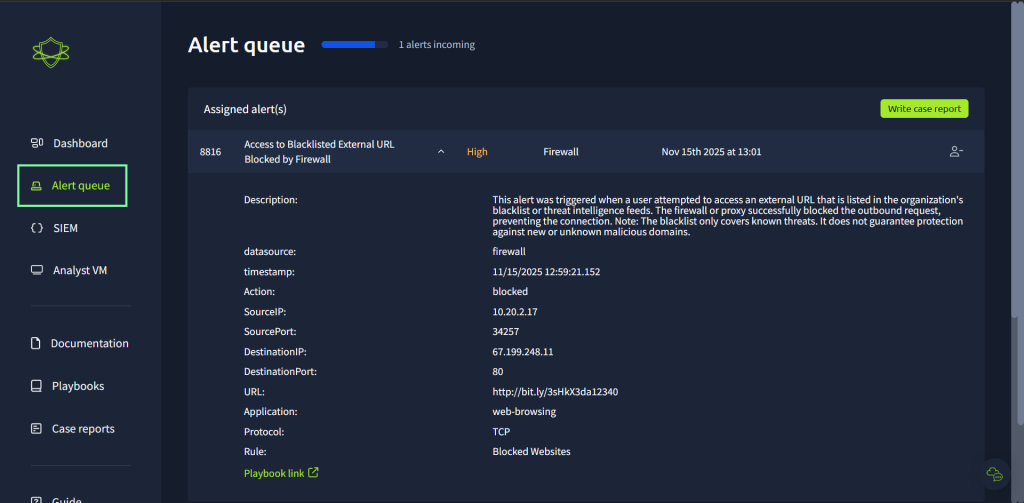

For the first assigned alert, it was obviously a true positive due to the rule. I recommend taking a screenshot of what I did below to write your report. My report passed. You might have to repeat yourself on some of what they expect but no big deal. Now it’s on to the next alert!

The next two on the list contain the same content and they are back-to-back. However, the sender and contents seem legit. What do you think?

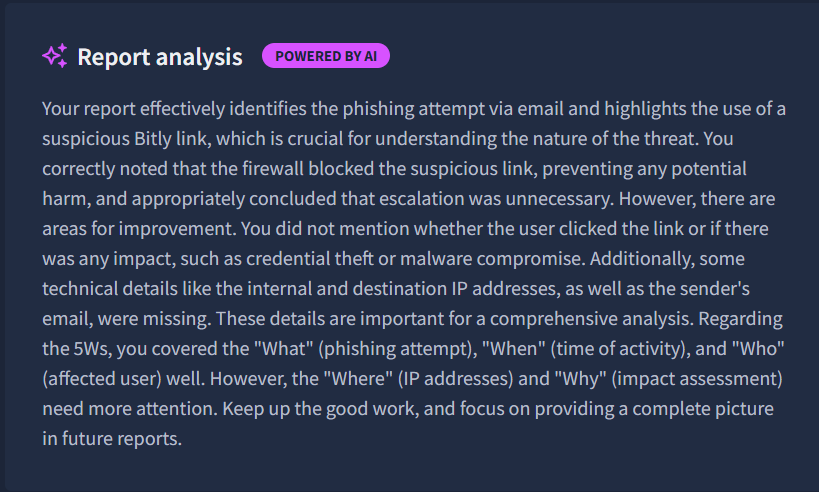
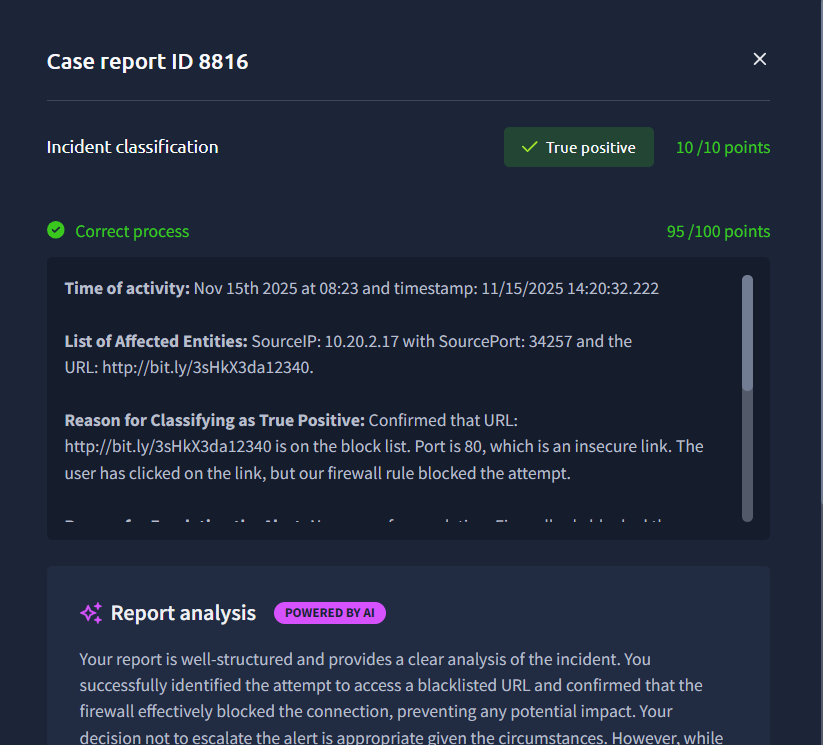
In the end, I ended up fumbling a little bit with my report writing. I ended up scoring lower than I wanted on points, so I went back and re-did it with the analysis in my mind. Most importantly, the 5 W’s.
“In terms of the 5Ws, you covered the ‘What’, ‘When’, and partially the ‘Who’, but the ‘Where’ and ‘Why’ need more detail. Focus on providing a comprehensive analysis that addresses all these aspects in future reports.” After I redid I was happy to see my scores go up!