
https://tryhackme.com/room/sysmon
Created by: tryhackme, 1337rce, TactfulTurtle
This is a recommended optional room for the SOC1 path. I thought, “More exposure to sysmon couldn’t hurt!”. Task 2, Sysmon Overview, goes over various config events with set conditions to trigger alerts.

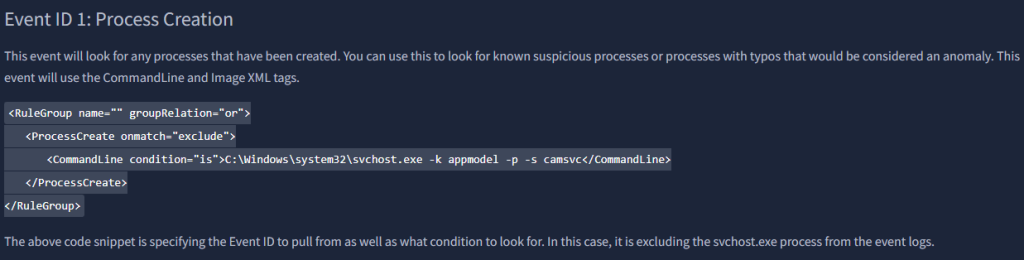
In Task 4, we are going to use PowerShell and Get-WinEvent, and/or weutil.exe. THM also suggests we check out another room, https://tryhackme.com/room/windowseventlogs, to get a more detailed experience with these tools.
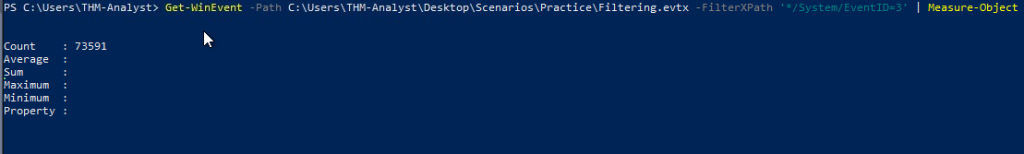
“How many event ID 3 events are in C:\Users\THMAnalyst\Desktop\Scenarios\Practice\Filtering.evtx?”
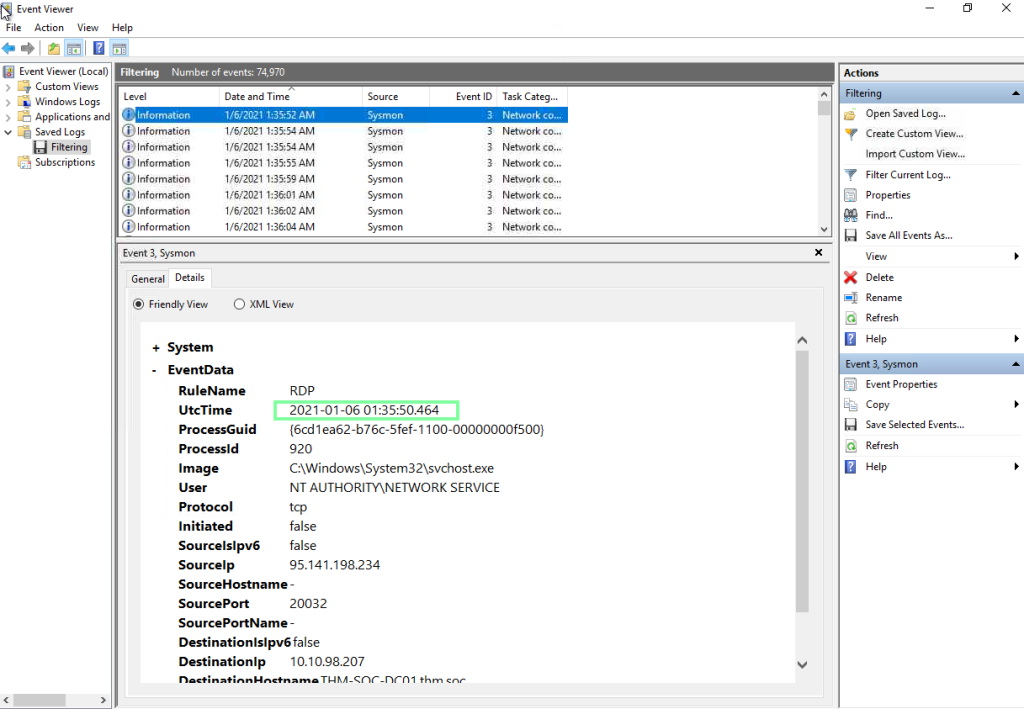
“What is the UTC of the first network event in the same logfile? Note that UTC is shown only in the “Details” tab.” I tried getting this within Powershell but I could never get the time to convert to UTC. In order to bring up the time, I used the command: Get-WinEvent -Path C:\Users\THM-Analyst\Desktop\Scenarios\Practice\Filtering.evtx -FilterXPath ‘*/System/EventID=3’ | Select-Object -First 1 | Format-List *
I ended up going to Event Viewer, as the question mentions “Details tab”, and got it easily from there. Once you open Event Viewer, go to “Open Saved Log” > Desktop > Practice > Filtering.
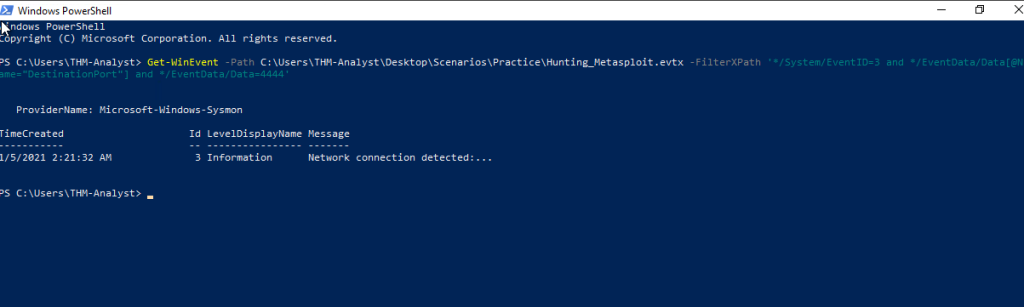
On to task 5, Hunting Metasploit!

THM has us look at Metasploit events through the Event Viewer, as well as through PowerShell.

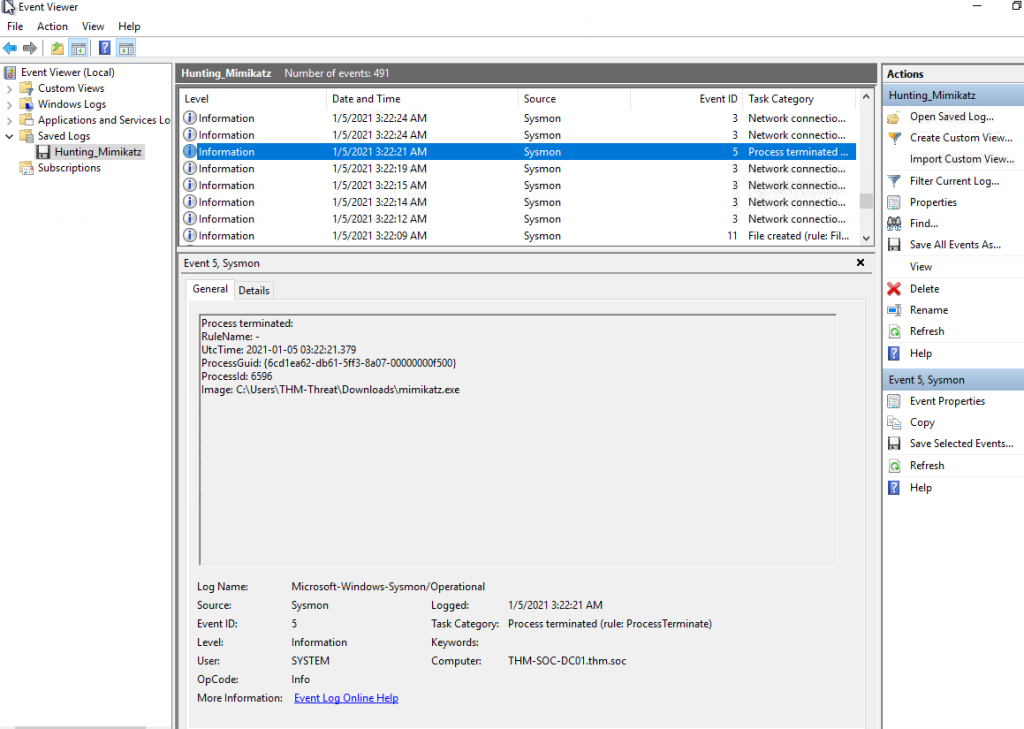
On to Task 6, Detecting Mimikatz!

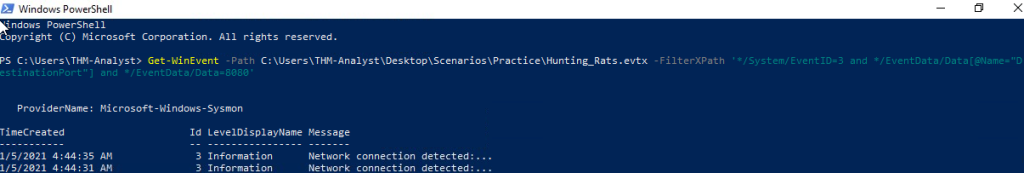
On to Task 7, Hunting Malware!

On to Task 8, Hunting Persistence!

On to Task 9, Detecting Evasion Techniques!


“What is the full registry key of the USB device calling svchost.exe in Investigation 1?”
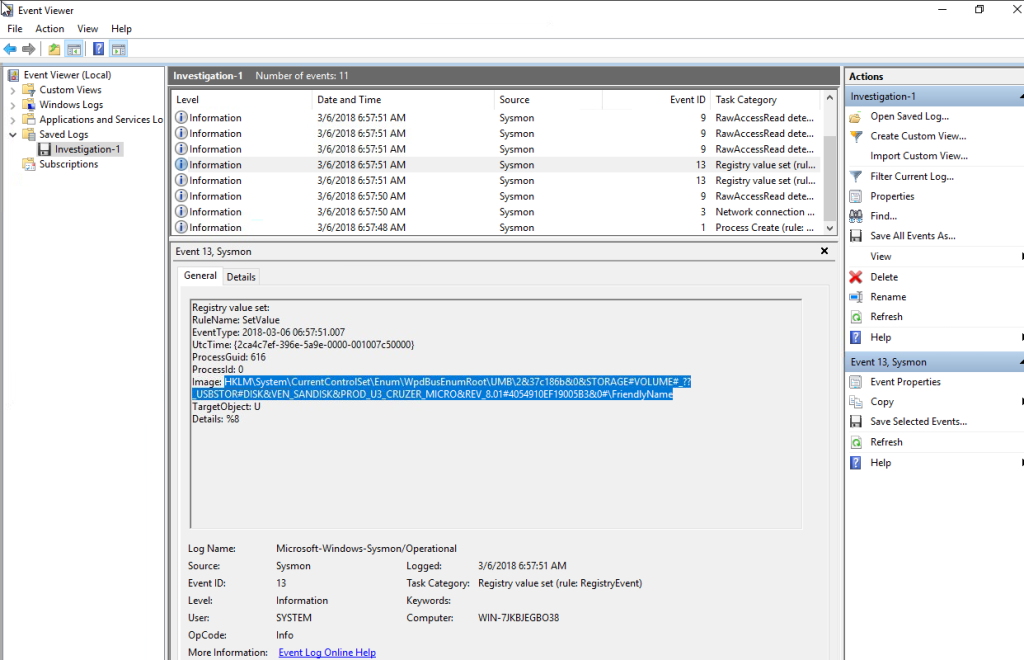
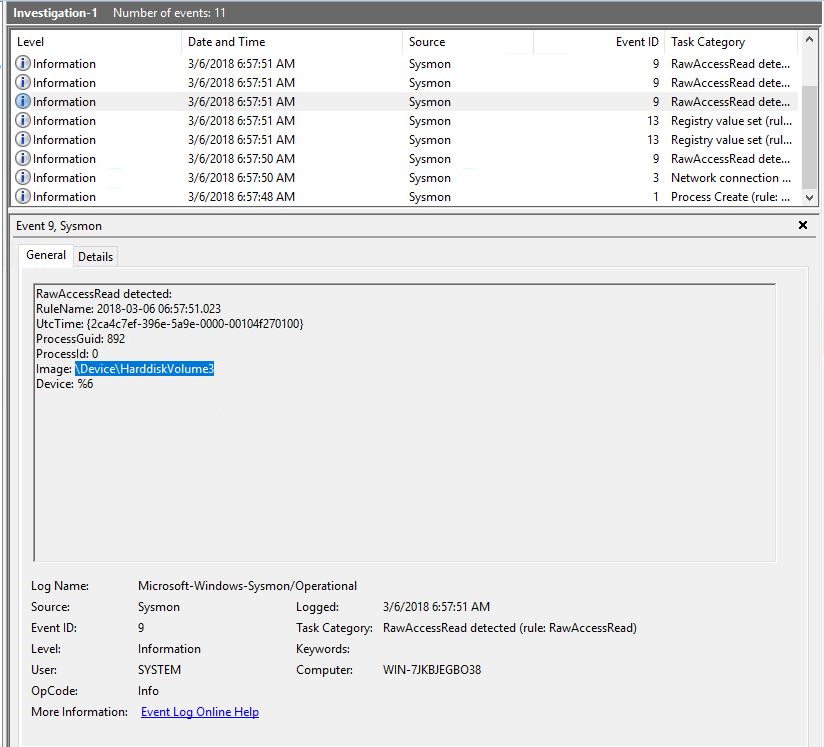
“What is the device name when being called by RawAccessRead in Investigation 1?”
“What is the first exe the process executes in Investigation 1?”

“What is the full path of the payload in Investigation 2?”
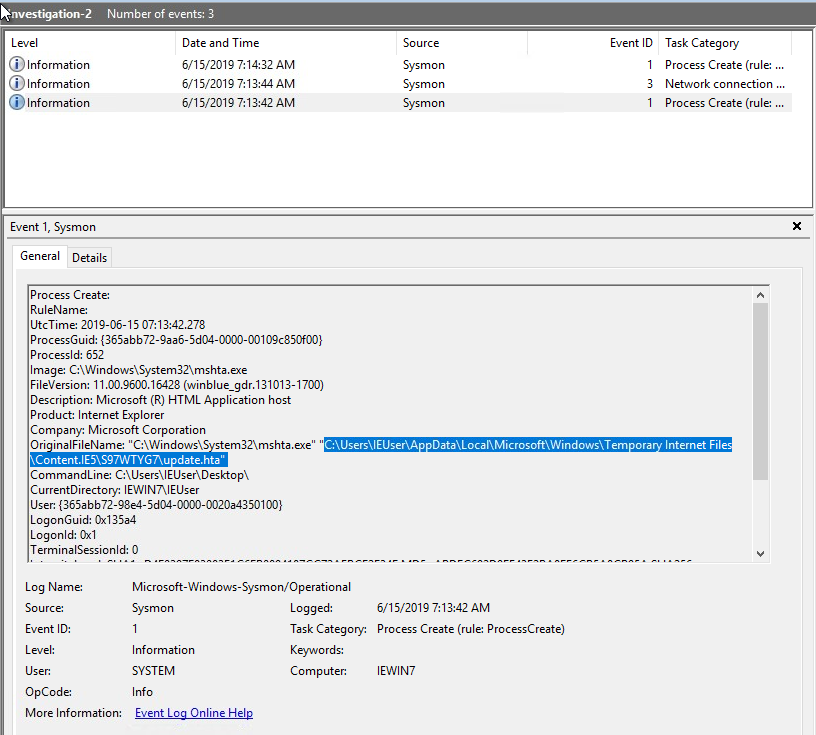
“What is the full path of the file the payload masked itself as in Investigation 2?”
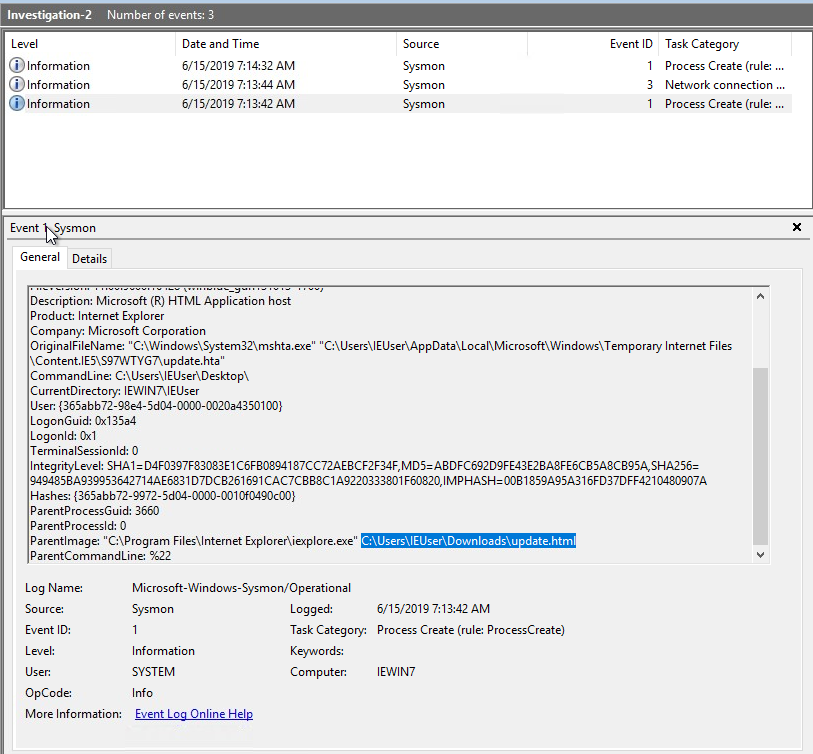
“What signed binary executed the payload in Investigation 2?”

“What is the IP of the adversary in Investigation 2?”

“What back connect port is used in Investigation 2?”
4443
“What is the IP of the suspected adversary in Investigation 3.1?”
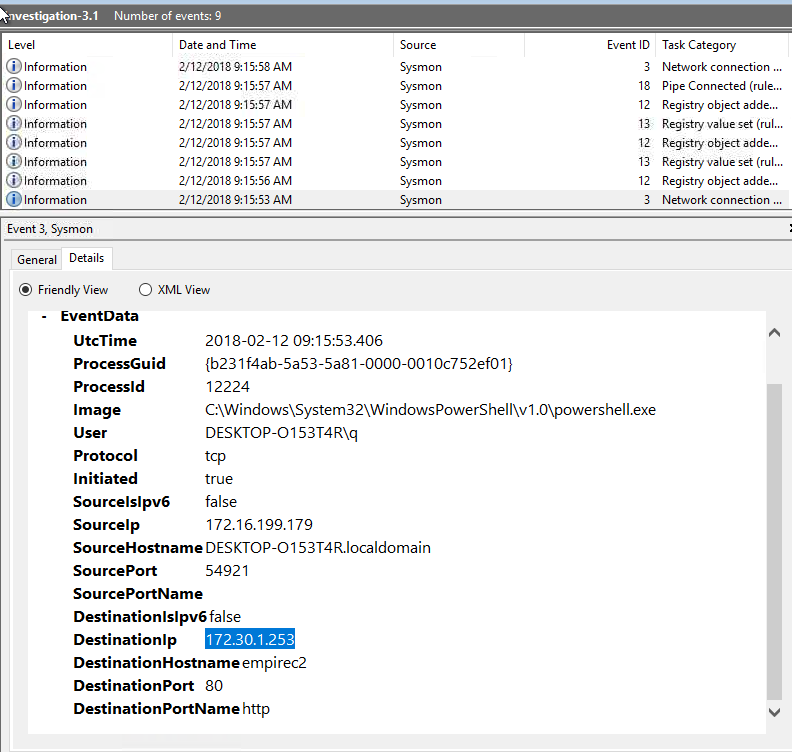
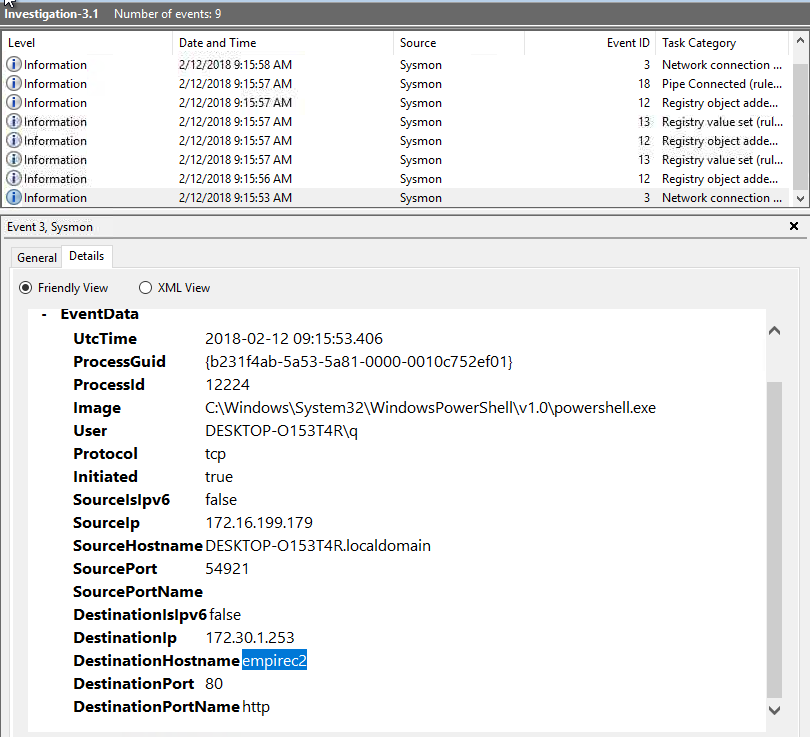
“”What is the hostname of the affected endpoint in Investigation 3.1?”

“What is the hostname of the C2 server connecting to the endpoint in Investigation 3.1?”
“Where in the registry was the payload stored in Investigation 3.1?”
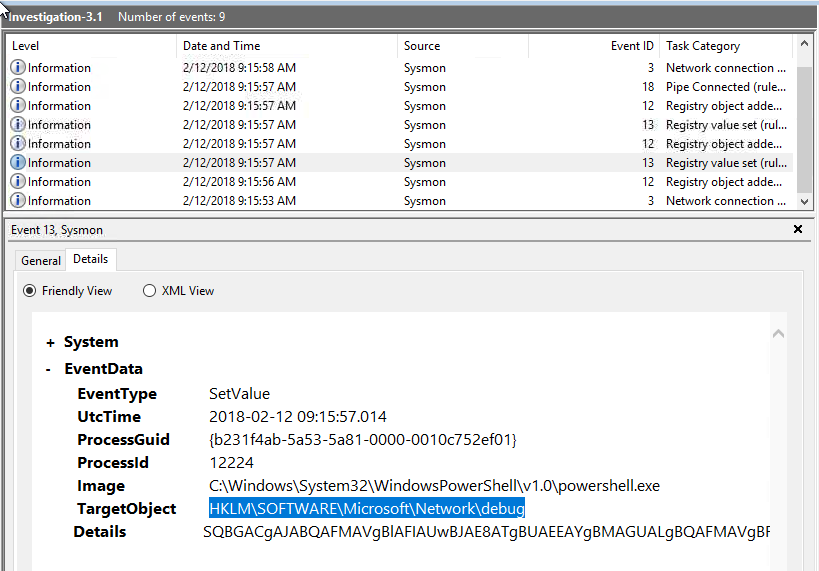
“What PowerShell launch code was used to launch the payload in Investigation 3.1?”
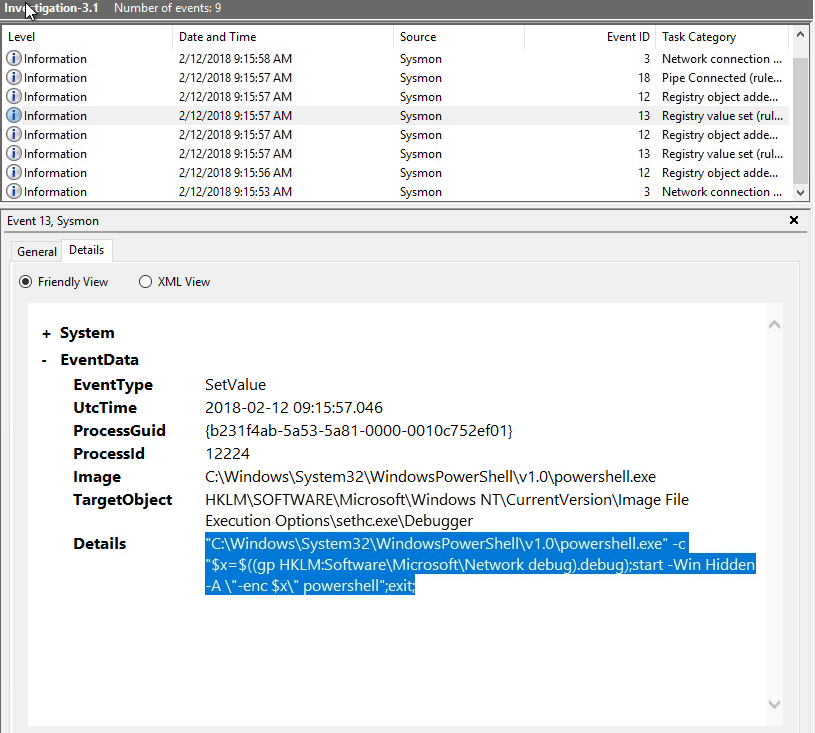
“What is the IP of the adversary in Investigation 3.2?”
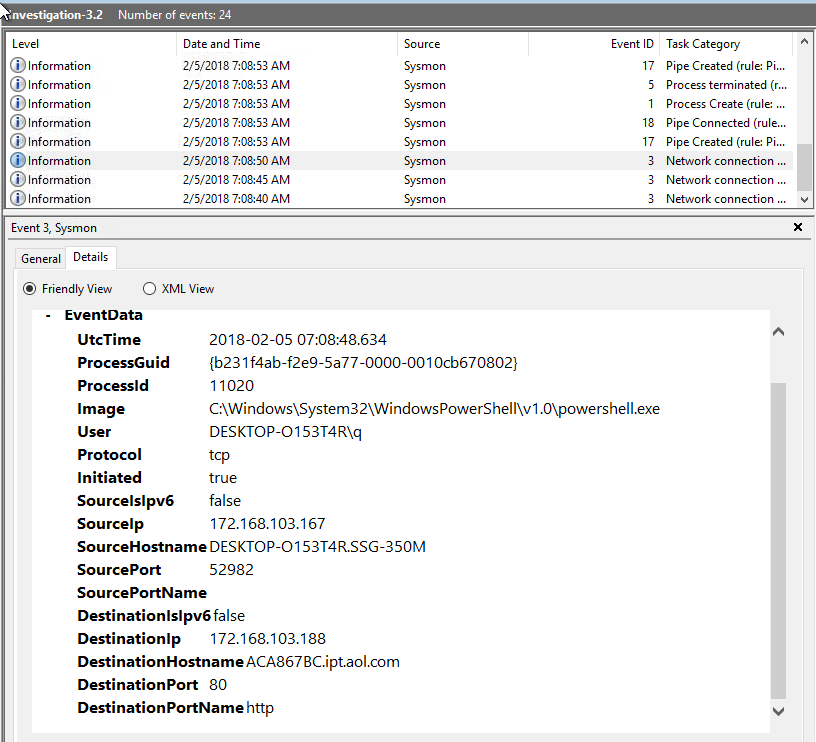
“What is the full path of the payload location in Investigation 3.2?”
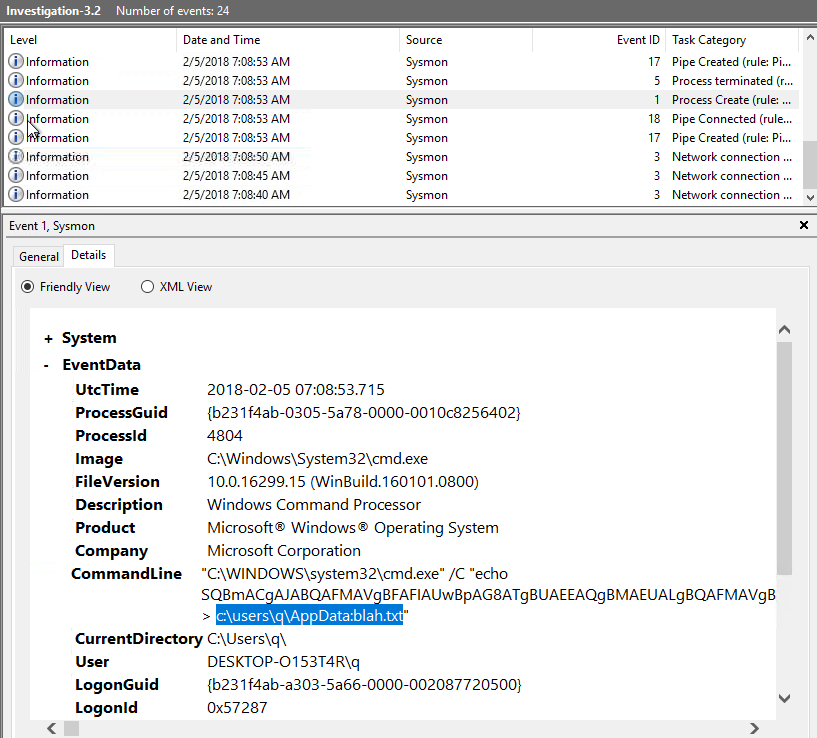
“What was the full command used to create the scheduled task in Investigation 3.2?”
I believe I deleted my screenshot of this, but it’s:
“C:\WINDOWS\system32\schtasks.exe” /Create /F /SC DAILY /ST 09:00 /TN Updater /TR “C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe -NonI -W hidden -c \”IEX ([Text.Encoding]::UNICODE.GetString([Convert]::FromBase64String($(cmd /c ”more < c:\users\q\AppData:blah.txt”’))))\””
“What process was accessed by schtasks.exe that would be considered suspicious behavior in Investigation 3.2?”

“What is the IP of the adversary in Investigation 4?”
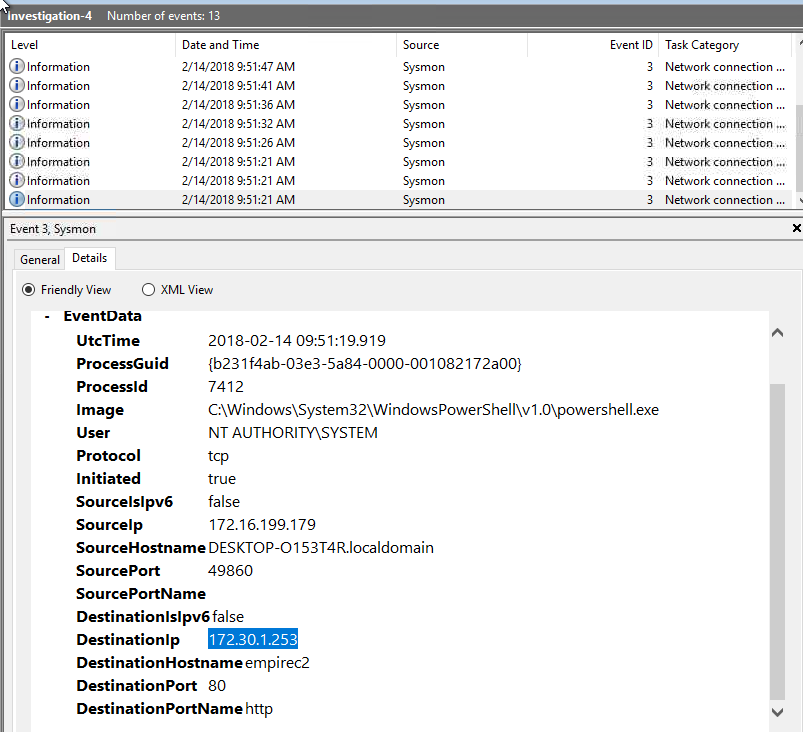
“What port is the adversary operating on in Investigation 4?”
80
“What C2 is the adversary utilizing in Investigation 4?”
empire