
https://tryhackme.com/room/networkminer
Created by:tryhackme, str3g4tt4, Gensane, TactfulTurtle
Per official description, “NetworkMiner is an open source Network Forensic Analysis Tool (NFAT) for Windows (but also works in Linux / Mac OS X / FreeBSD). NetworkMiner can be used as a passive network sniffer/packet capturing tool to detect operating systems, sessions, hostnames, open ports etc., without putting any traffic on the network. NetworkMiner can also parse PCAP files for offline analysis and to regenerate/reassemble transmitted files and certificates from PCAP files.
NetworkMiner has, since the first release in 2007, become a popular tool among incident response teams as well as law enforcement. NetworkMiner is today used by companies and organizations all over the world.”

You are probably thinking what I am thinking: “Why not just use Wireshark?” As for me, that’s all I’ve heard about it when it comes to network sniffing. Well, per THM, “NetworkMiner and Wireshark have similar base features, but they differ in use purpose. Although the main functions are identical, some of the features are much stronger for specific use cases. The best practice is to record the traffic for offline analysis, quickly overview the pcap with NetworkMiner, and go deep with Wireshark for further investigation.”
NetworkMiner can do OS fingerprinting and Host Categorization, where Wireshark cannot.

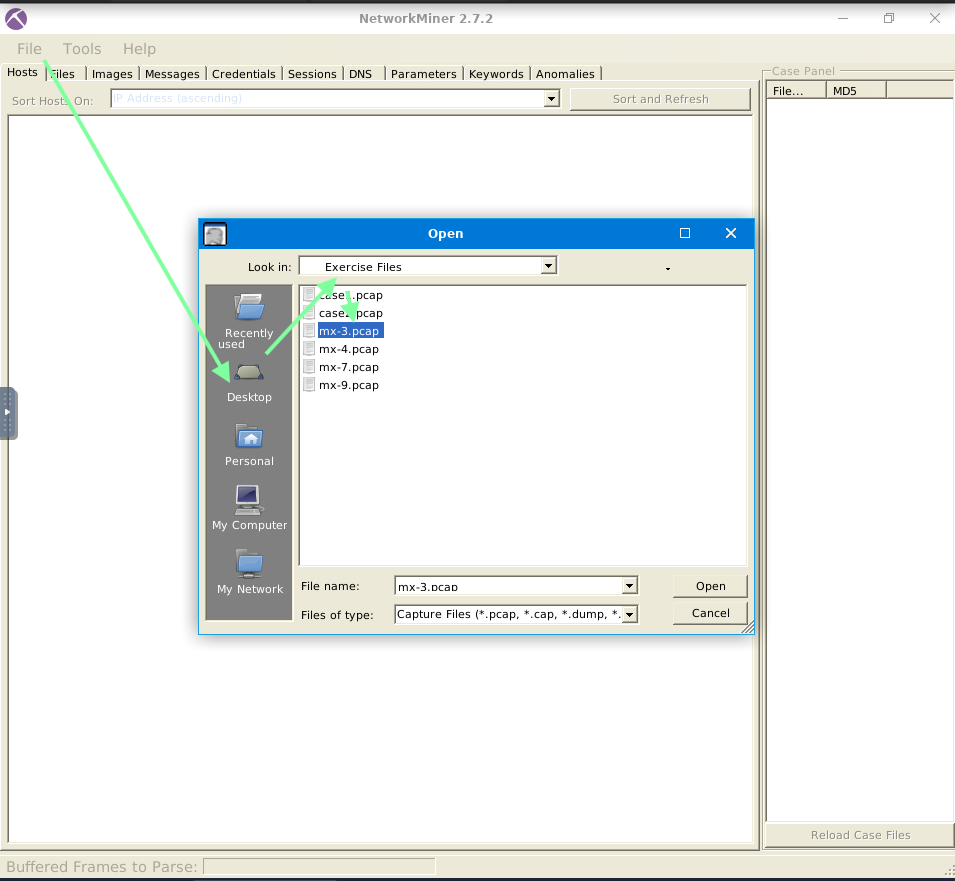
Tool Overview 1
“Use the “~/Desktop/Exercise Files/mx-3.pcap” file to answer the questions below. What is the total number of frames?”
What is the total number of frames?”
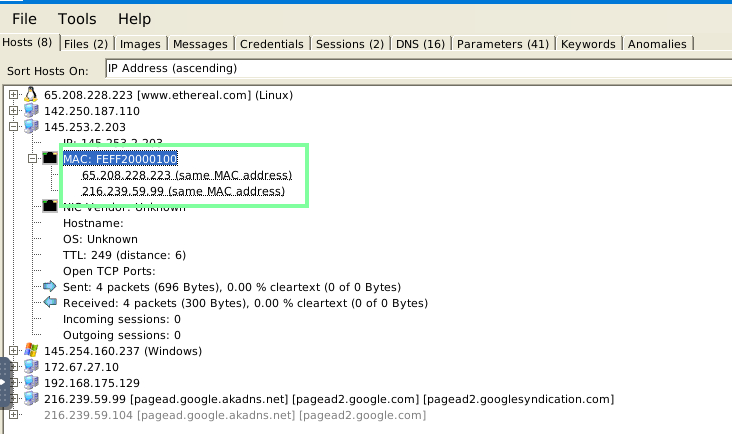
“How many packets were sent from host 65.208.228.223?”

“What is the name of the webserver banner under host 65.208.228.223?”

“Use the “~/Desktop/Exercise Files/mx-4.pcap” file to answer the questions below.
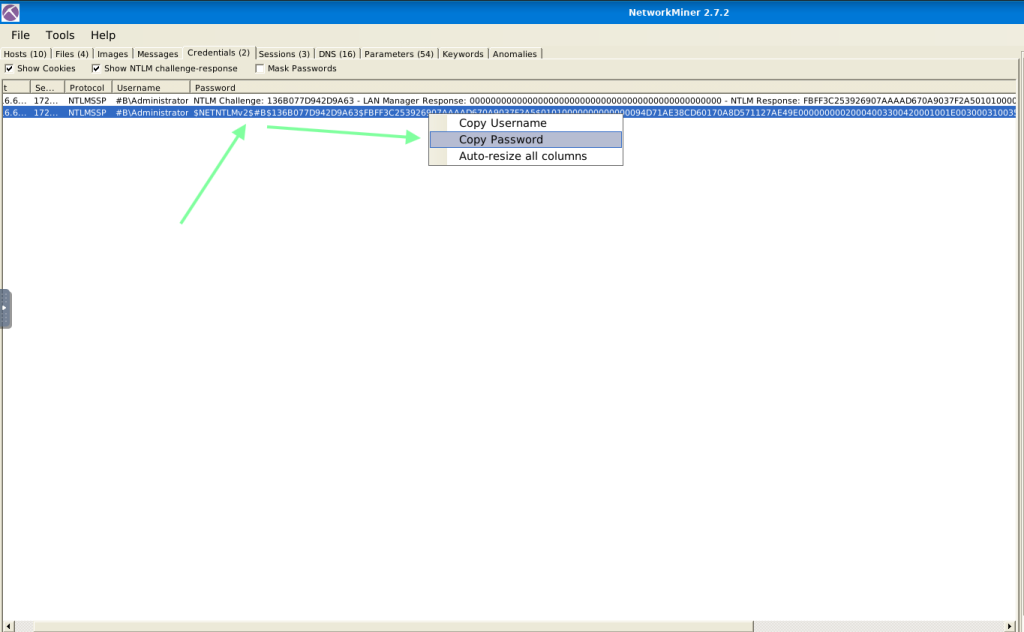
What is the extracted username for the 02694W-WIN10 host?”
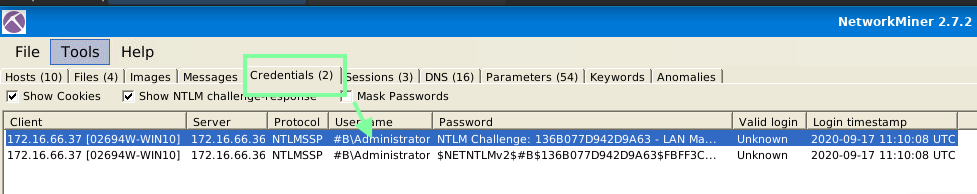
“What is the extracted password for the user logged into the 02694W-WIN10 host? Enter the full NTLM hash.”
Tool Overview 2
“Use “~/Desktop/Exercise files/mx-7 pcap” file to answer the questions below
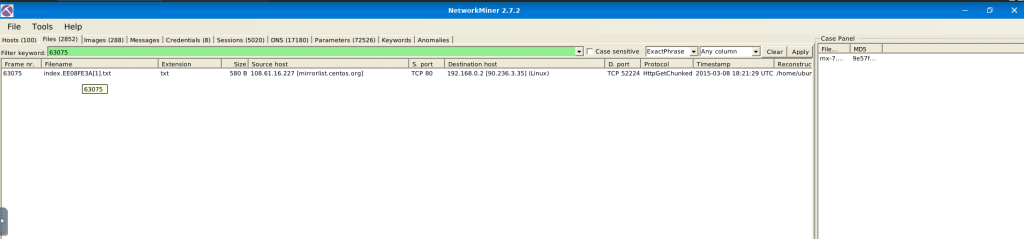
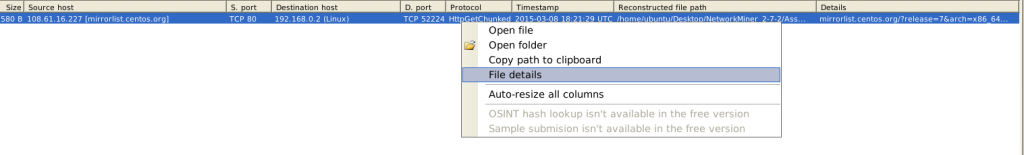
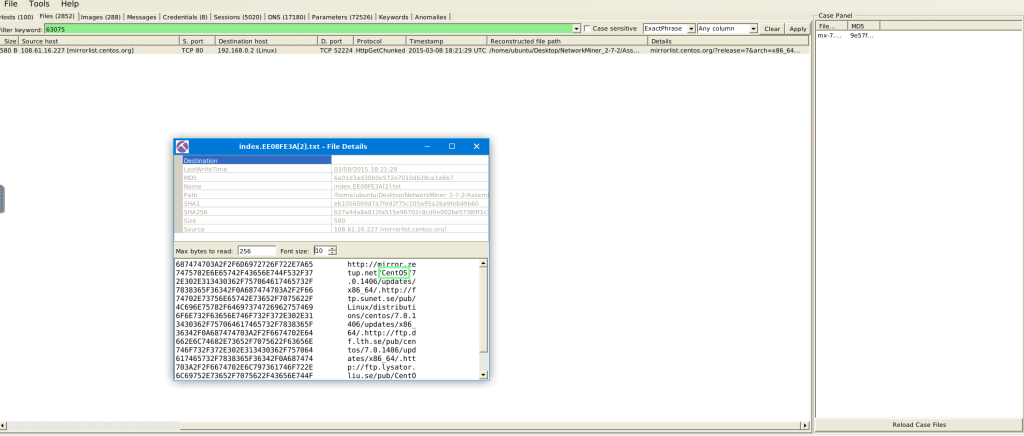
What is the name of the Linux distro mentioned in the file associated with frame 63075?”
So for the life of me this would not pull up no matter how I searched it(through the filter or manually) and remembered that THM does state this might happen earlier on during the lab. If this does happen to you, close out of the software and then relaunch the file and try again.
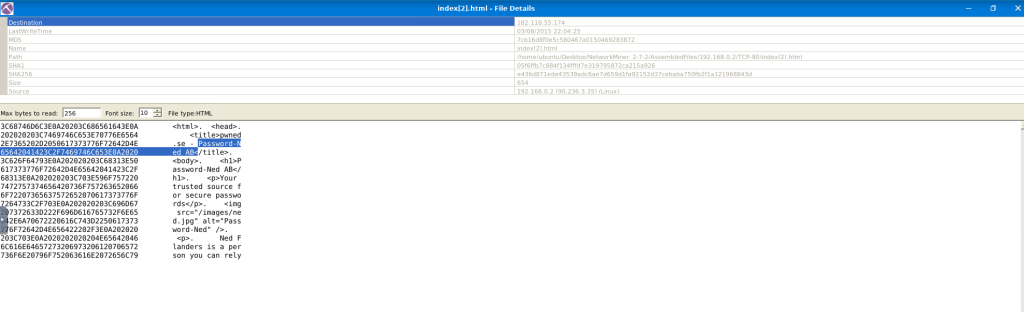
“What is the header of the page associated with frame 75942?”
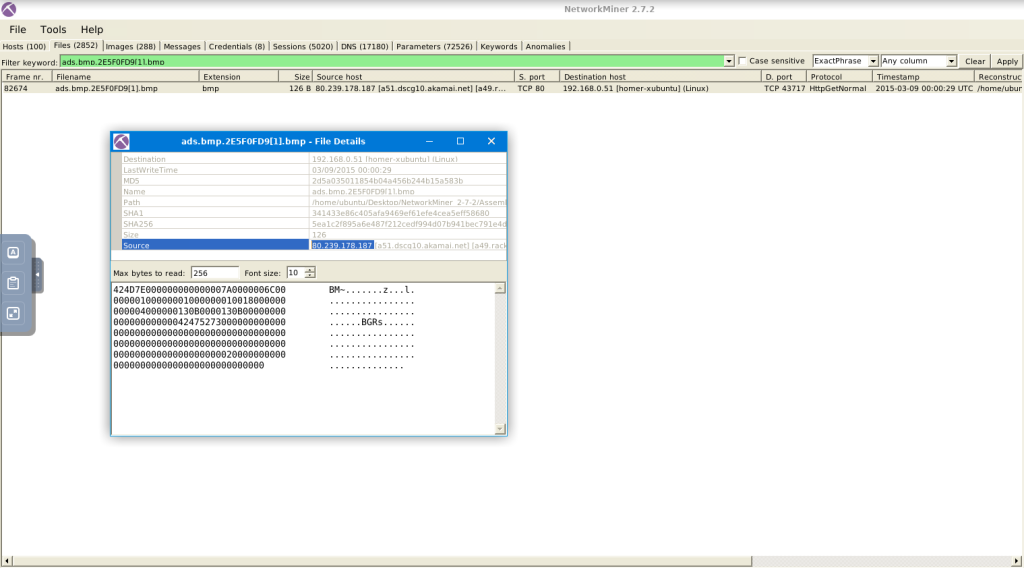
“What is the source address of the image “ads.bmp.2E5F0FD9[1].bmp”?”
“What is the frame number of the possible TLS anomaly?”
Anomaly is the keyword in searching for this. I was looking it up in the Sessions tab at first but then quickly found it when switching tabs!

“Use “~/Desktop/Exercise files/mx-9” file to answer the questions below
Look at the messages. Which platform sent an email with the subject starting with “You have more”?”

“What is the email address of Branson Matheson?”

In task 6, Version Differences, THM covers the difference between version 1.6 and version 2.7. They took a lot of the detailed stuff after 1.6. I am guessing instead of competing with Wireshark, they focused on other angles of packet capturing.
Task Excercises!
“Use the “~/Desktop/Exercise Files/case1.pcap” file to answer the questions below.
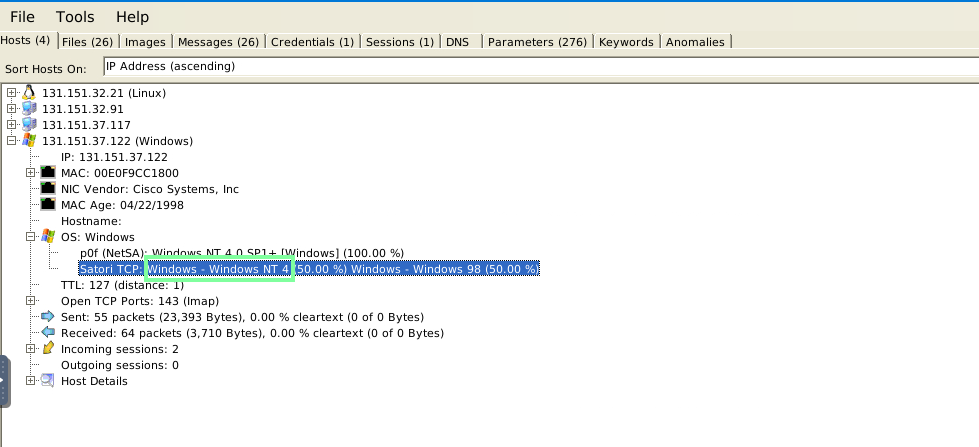
What is the OS name of the host 131.151.37.122?”
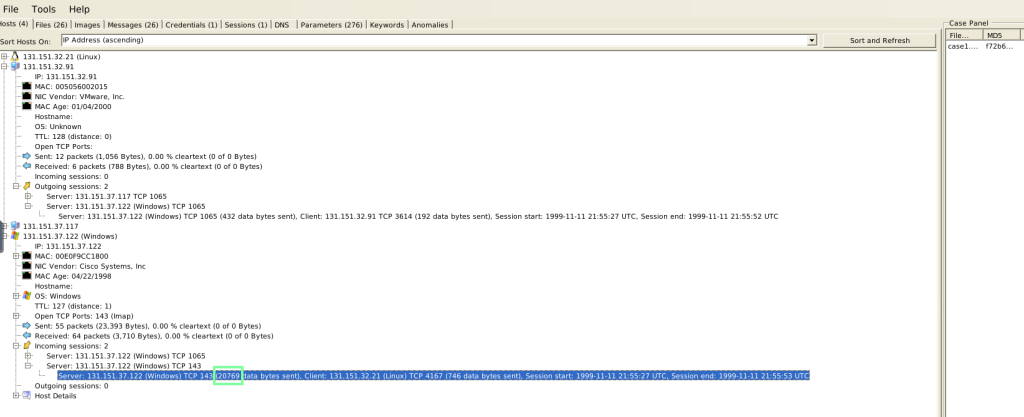
“Investigate the hosts 131.151.37.122 and 131.151.32.91.
How many data bytes were received from host 131.151.32.91 to host 131.151.37.122 through port 1065?”

“Investigate the hosts 131.151.37.122 and 131.151.32.21.
How many data bytes were received from hos 131.151.37.122 to host 131.151.32.21 through port 143?”
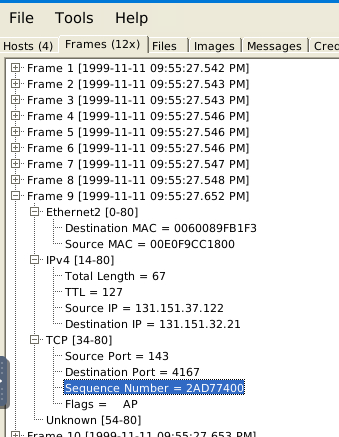
“What is the sequence number of frame 9?” You will need to switch to NetworkMiner 1.61 for this!
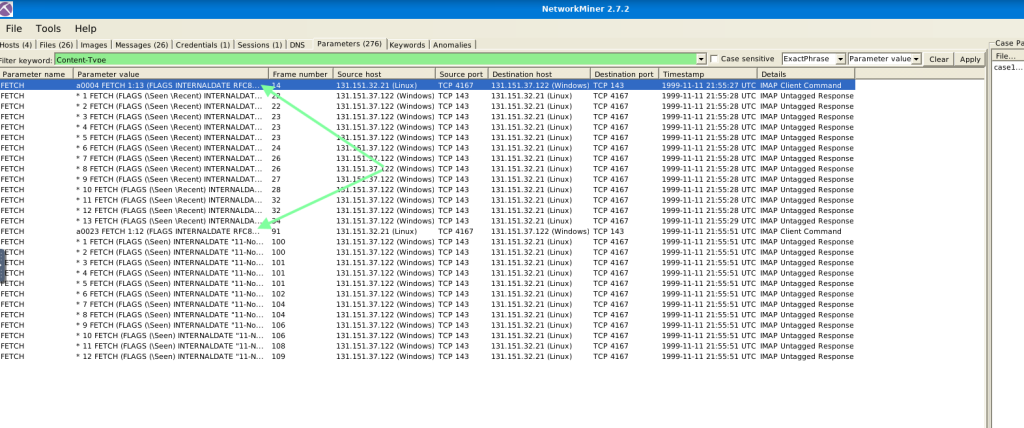
What is the number of the detected “content types”? It will be 2.
“Use the “~/Desktop/Exercise Files/case2.pcap” file to answer the questions below.
What is the USB product’s brand name?”

“What is the name of the phone model?”

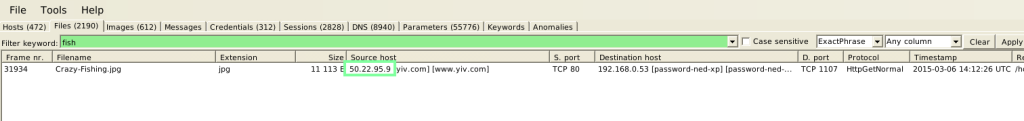
“What is the source IP of the fish image?”
What is the password of the “homer.pwned.se@gmx.com”?

“What is the DNS Query of frame 62001?”
