
https://tryhackme.com/room/ICS-modbus-aoc2025-g3m6n9b1v4
Created by: tryhackme, h4sh3m00, empandaL0ver
A lot of reading in this room, but it’s important reading. THM goes over the importance of the SCADA system in this room. Nation-state threat actors that have Advanced Persistent Threats(APT) abilities target SCADA systems.

“What port is commonly used by Modbus TCP?”

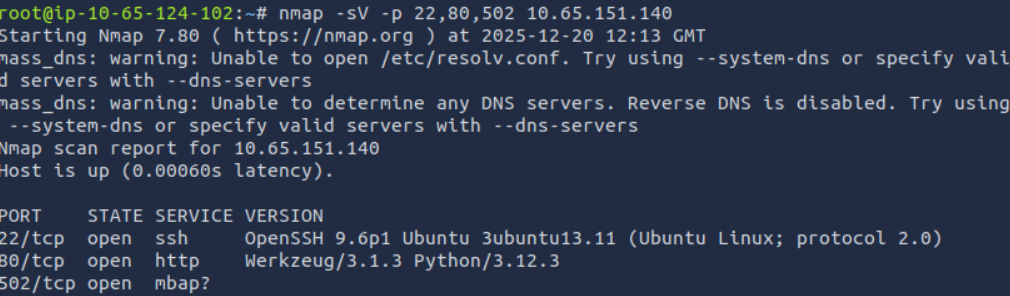
After a considerable amount of reading, we are now at the practical task. First off, we run an nmap scan. This might take a minute or two to complete. The 502 is our Modbus port.
Now we are instructed to go the web app where we can see CCTV footage and to our surprise our warehouse has been compromised!

THM uses the Python interpreter in the terminal to connect to the Modbus interface. If you are new to Python, don’t fret if a lot of this seems like gibberish to you. The simplified wording of what we are looking at is:
if elves have control = Christmas
or if the bunnies have control = Eggmas
Read a long, and you will start noticing the why and how the warehouse system has been messed with. Below you will see the elif statement that changes the package_type to 1, which is for chocolate eggs. So if bunnies have control = chocolate eggs for Christmas!
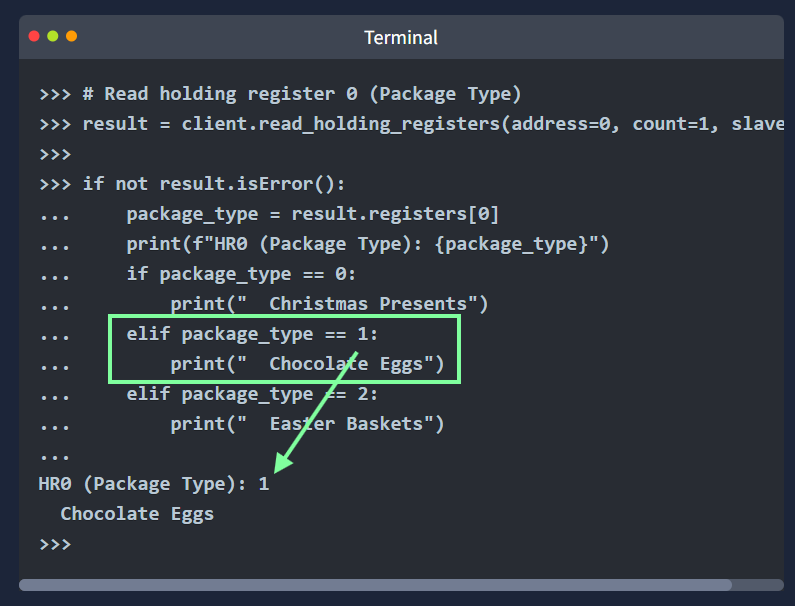
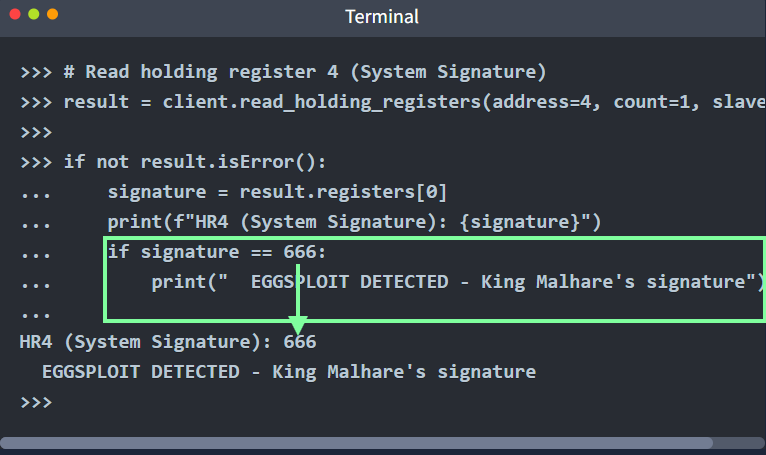
THM shows a few more examples of the compromised Modbus interface before tasking us with starting a Nano file, where we will copy and paste pre-written code.

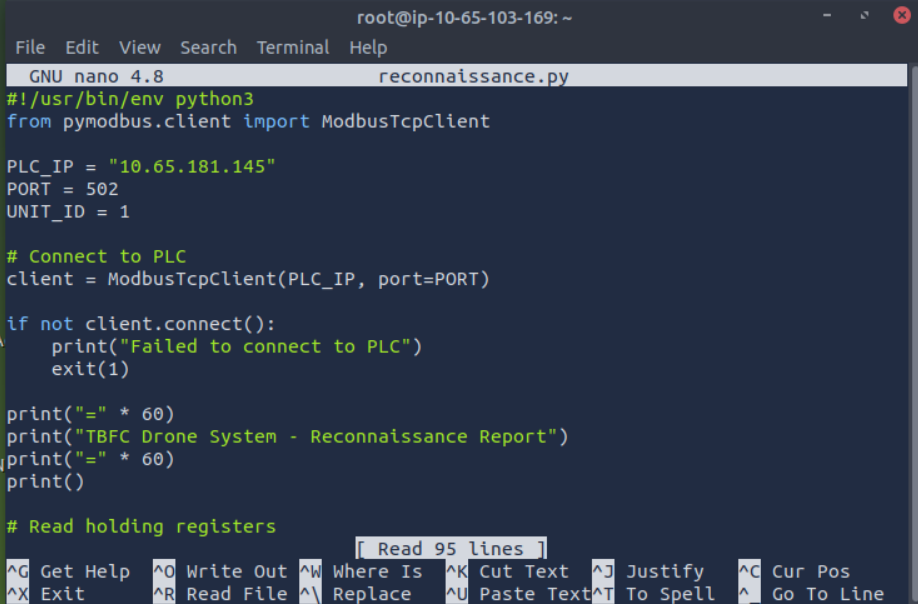

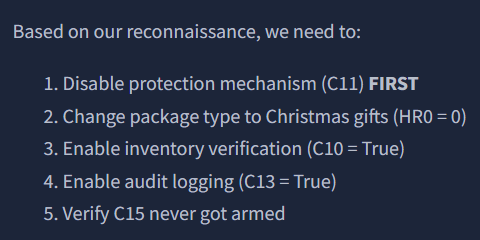
THM has us writing a new lengthy Python script. We need to copy and paste this to patch everything up and defeat Malhare. The script contains our flag as well!
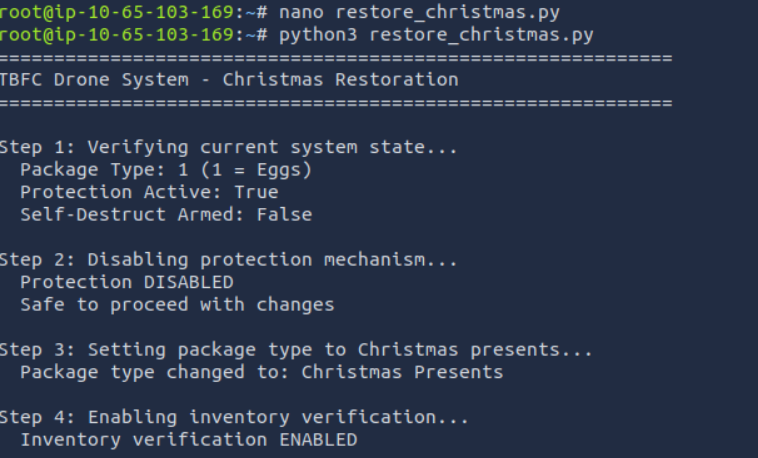
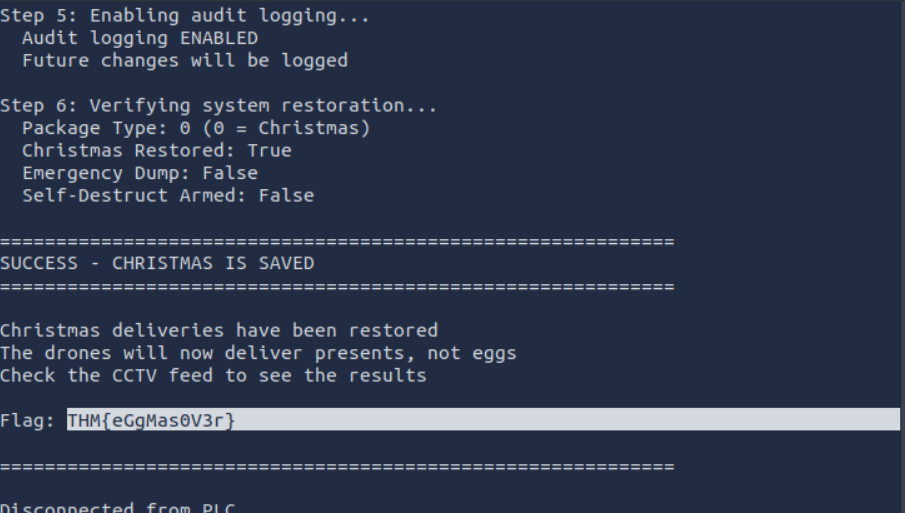
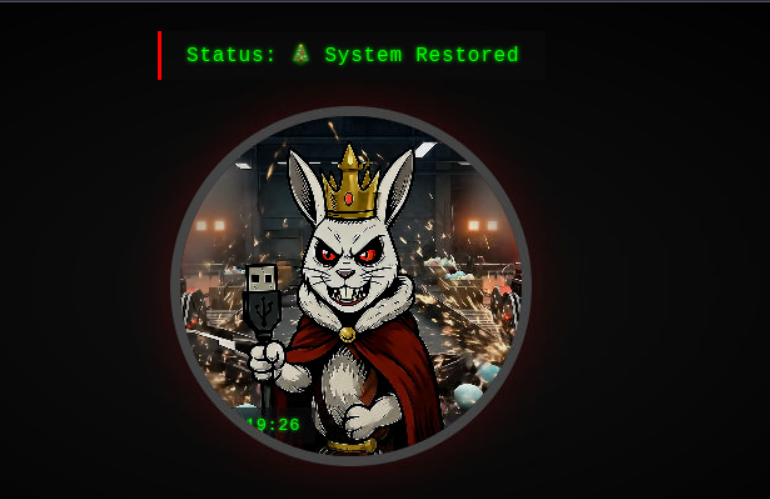
After this has been run, go back to the website, and we see that we pissed off the bunny king, but he looks like he has some plans scheming!
This was a pretty cool room and shows the importance of protecting SCADA systems.
“If you enjoyed today’s room, feel free to check out our OT challenge: Industrial Intrusion“