
https://tryhackme.com/room/obfuscation-aoc2025-e5r8t2y6u9
Created by: tryhackme, DrGonz0, arebel
Recommended THM walkthrough if you are new by TechAlisa: https://www.youtube.com/watch?v=FklTaBUqJrk
This room gives great examples of obfuscation through examples and has us see it play out in real time with CyberChef: https://gchq.github.io/CyberChef/.
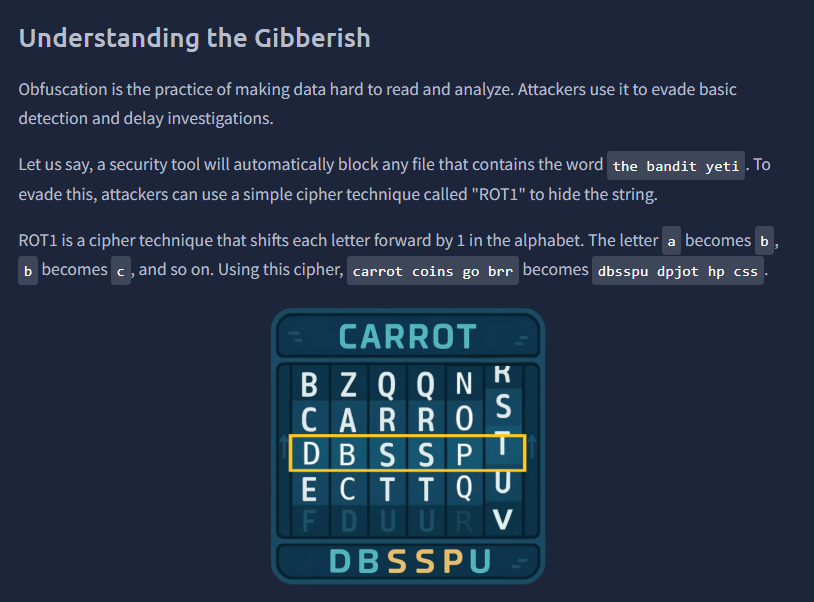
On Day 17, CyberChef was used extensively, so a lot of this is familiar to us. In this room, they break down the how and whys, which might clear some things if you are not familiar with obfuscation and how the CyberChef tool can aid us in de-obfuscating.
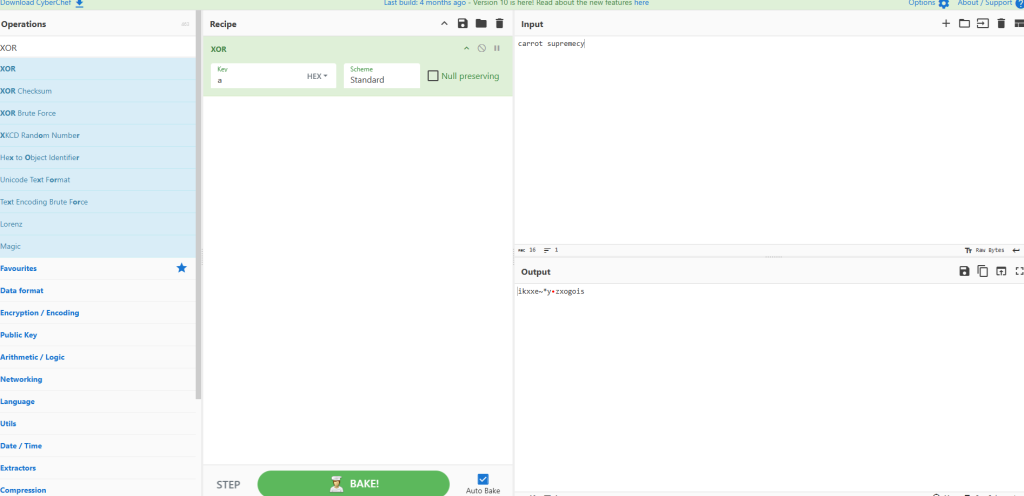
THM has us experiment with CyberChef to see an example.
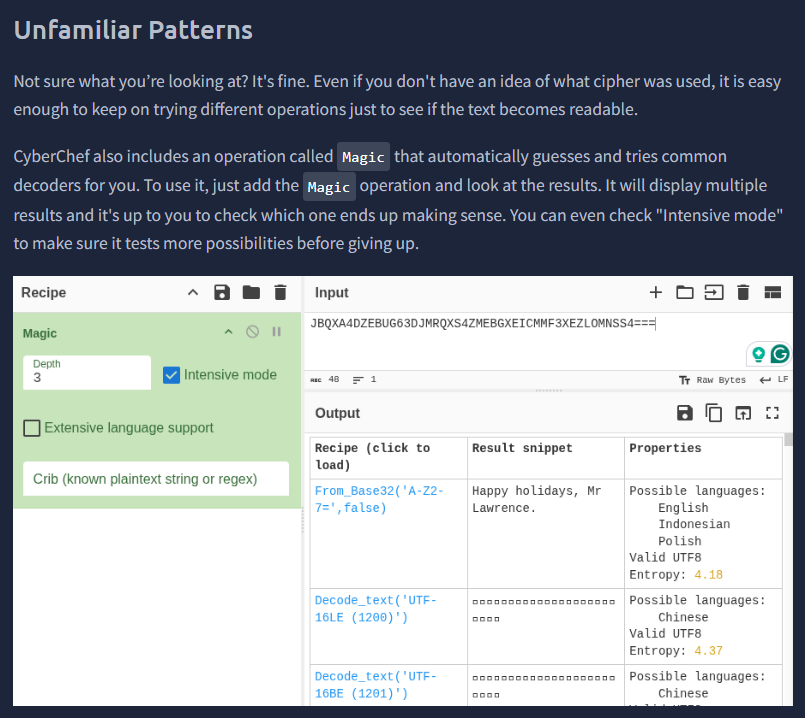
I’ve used CyberChef a good bit, but I was unfamiliar with the Magic recipe. This is pretty neat!
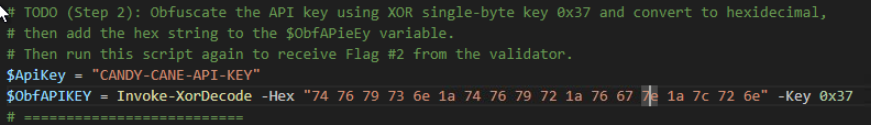
We are eventually tasked with opening a PowerShell script from the desktop and will end up running this in the PowerShell terminal. I suggest going full screen for this. Within the script, we have steps we are required to do. Don’t be intimidated by this script!


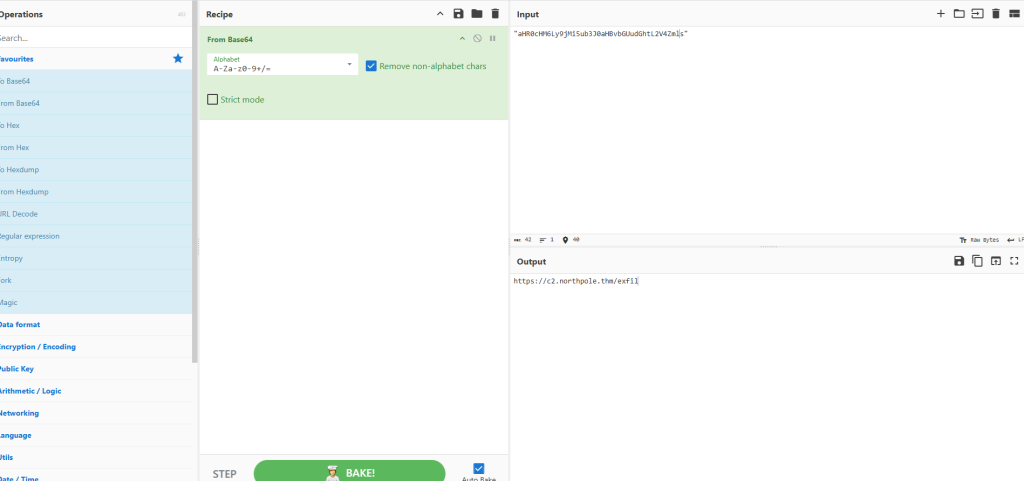
So now we need to input this into our script. Make sure you save it after the change. After that, launch PowerShell as instructed and run the script.
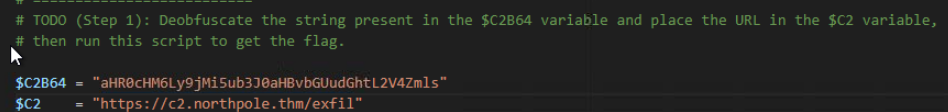
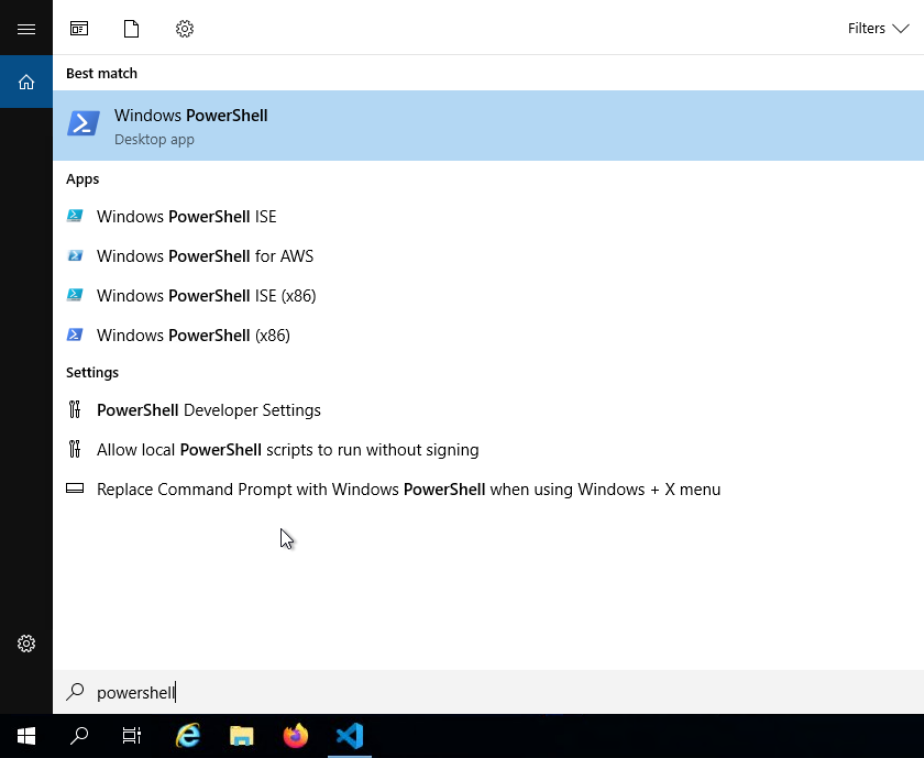

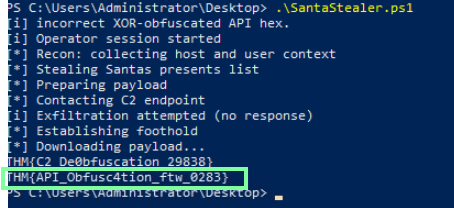
Running this script, we obtain our first flag!

On to Part 2!
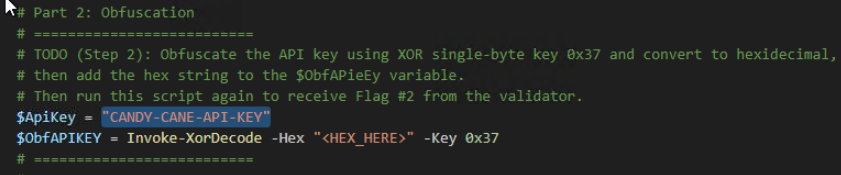

I do wish this room were longer and went into the script/PowerShell aspect more, but this is a good beginner room. If you do want to dive deeper, THM links to another room: “If you want to learn more about Obfuscation, check out our Obfuscation Principles room!”